Vaultica · version 2.5
The server that issues and checks the licences.
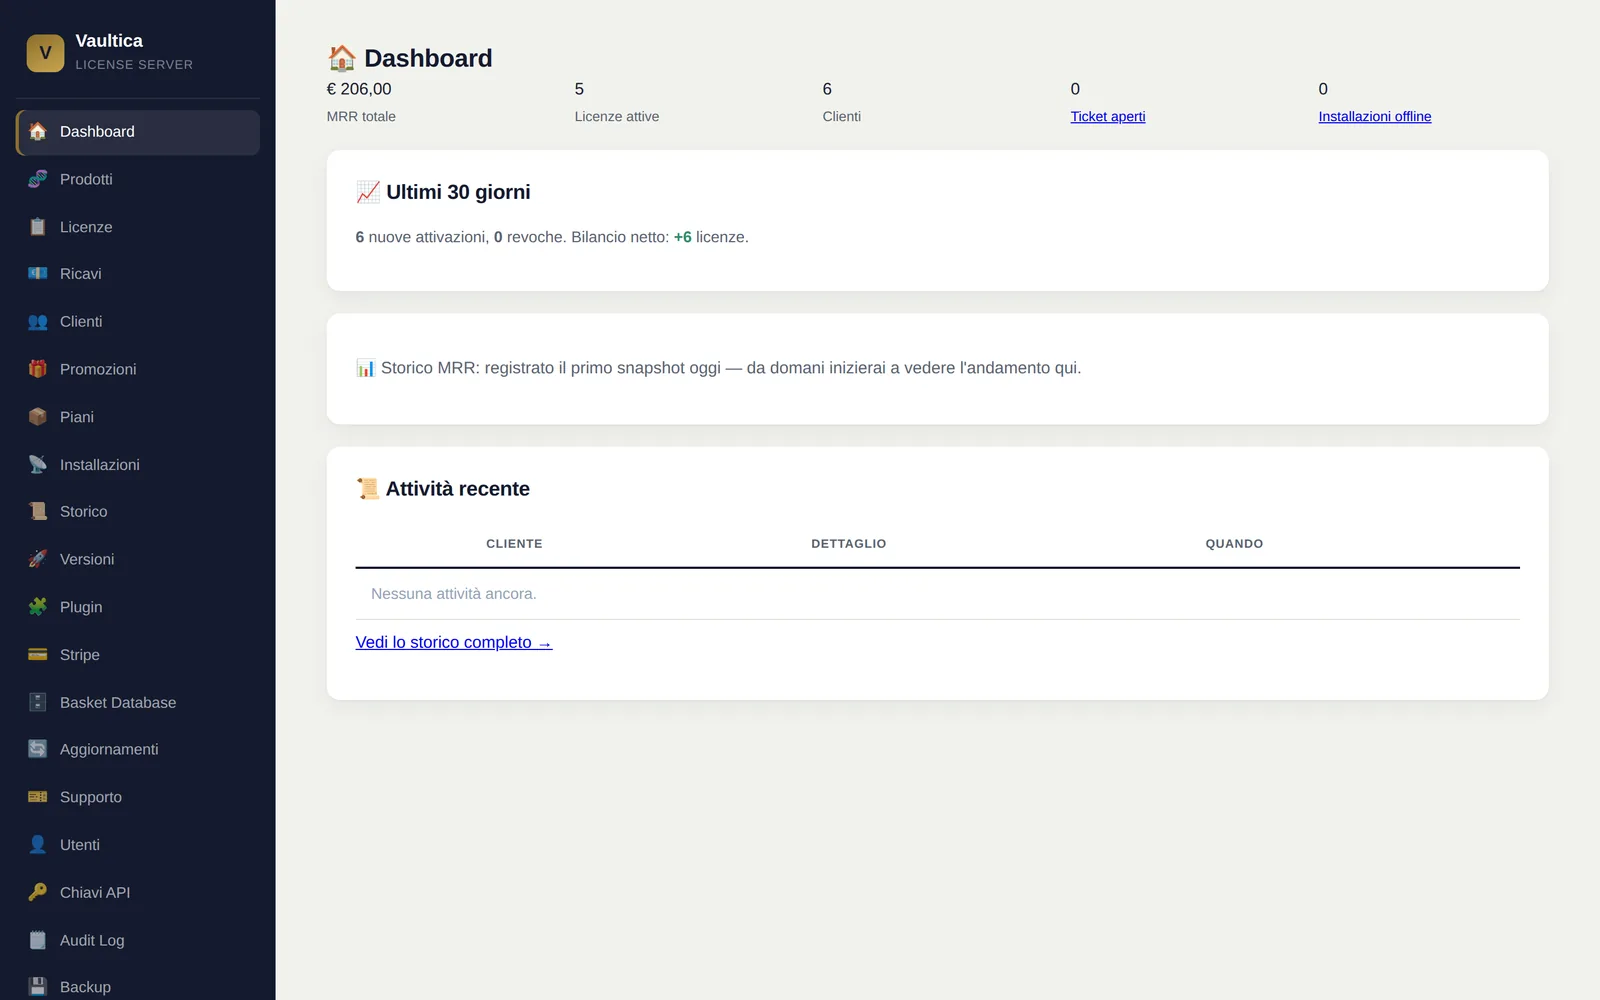
Vaultica issues licences, verifies them, keeps installations in view and shows the seller how things are going. Kondexa asks it whether a licence is valid and verifies the signature before trusting it.
Inside
What whoever issues the licences finds in it
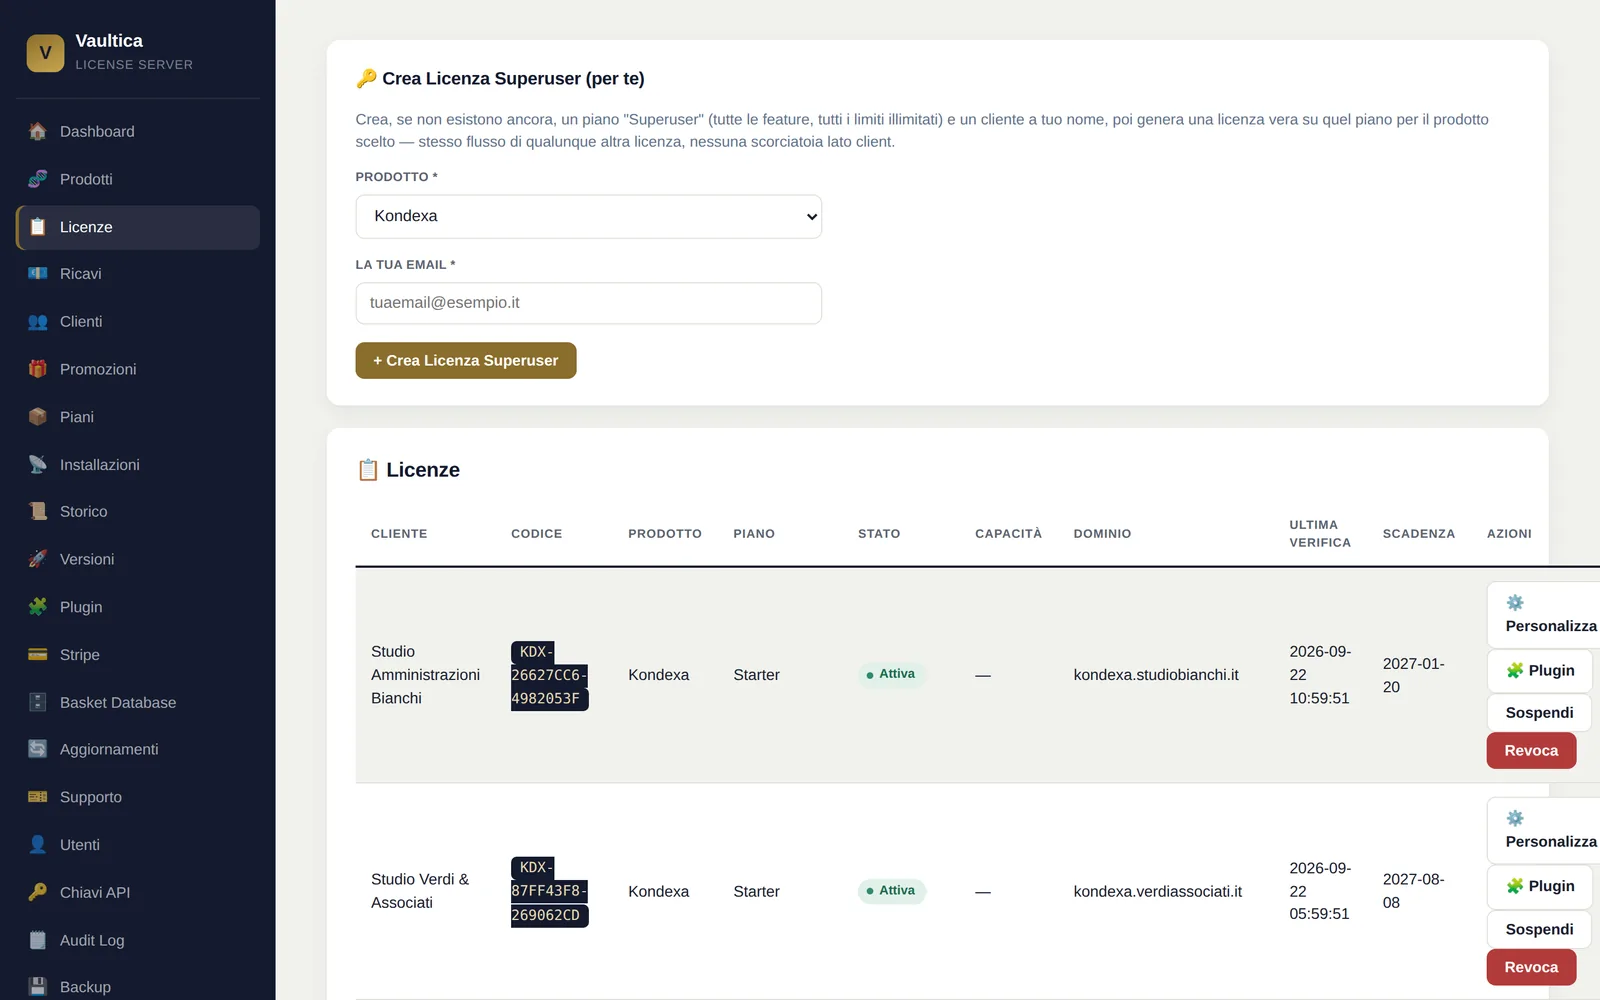
Licences
Every response is signed, and the product verifies it
The server RSA-signs what it answers, and the installed product verifies the signature before trusting it. A response altered on the way does not get through.
- An RSA signature on every server response
- The check lives in the product, not only in the server
- Each licence is tied to a customer and their plan
Installations
The heartbeat of every installation
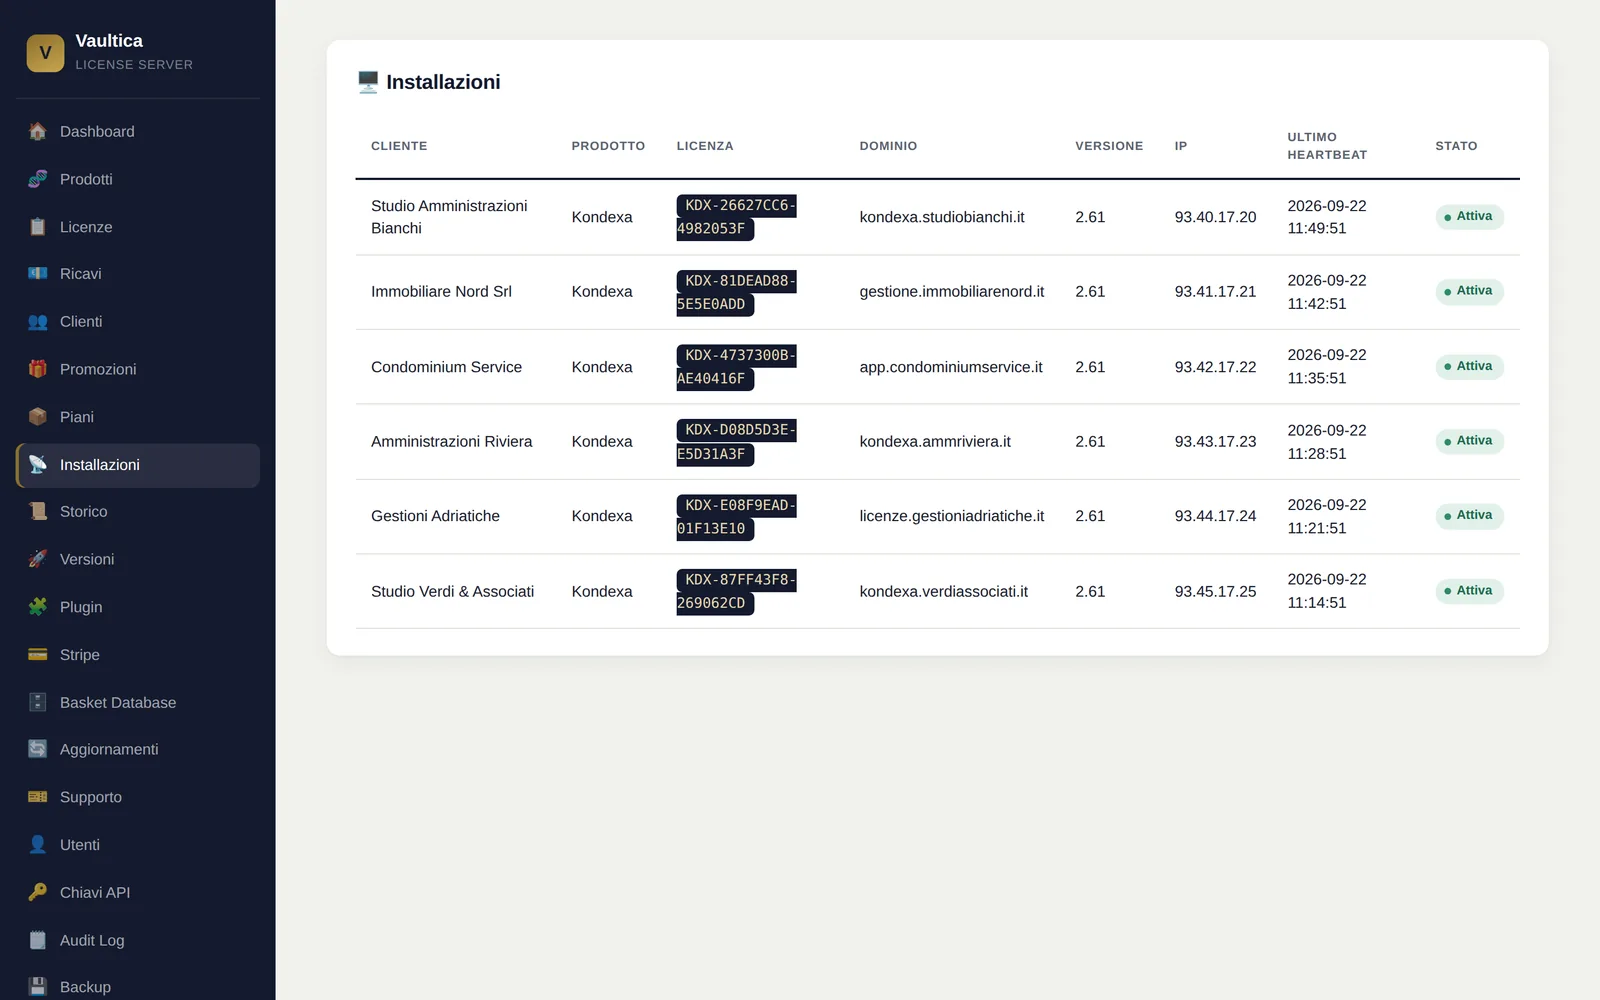
Every live installation sends a heartbeat. Domain, fingerprint, version and last contact stay visible in the panel: you see what is running, on which version and from where.
- The installation's domain and fingerprint
- The version running and the last contact
- Every installation attached to a licence, in one place
Plans
The plans, and the public page they produce
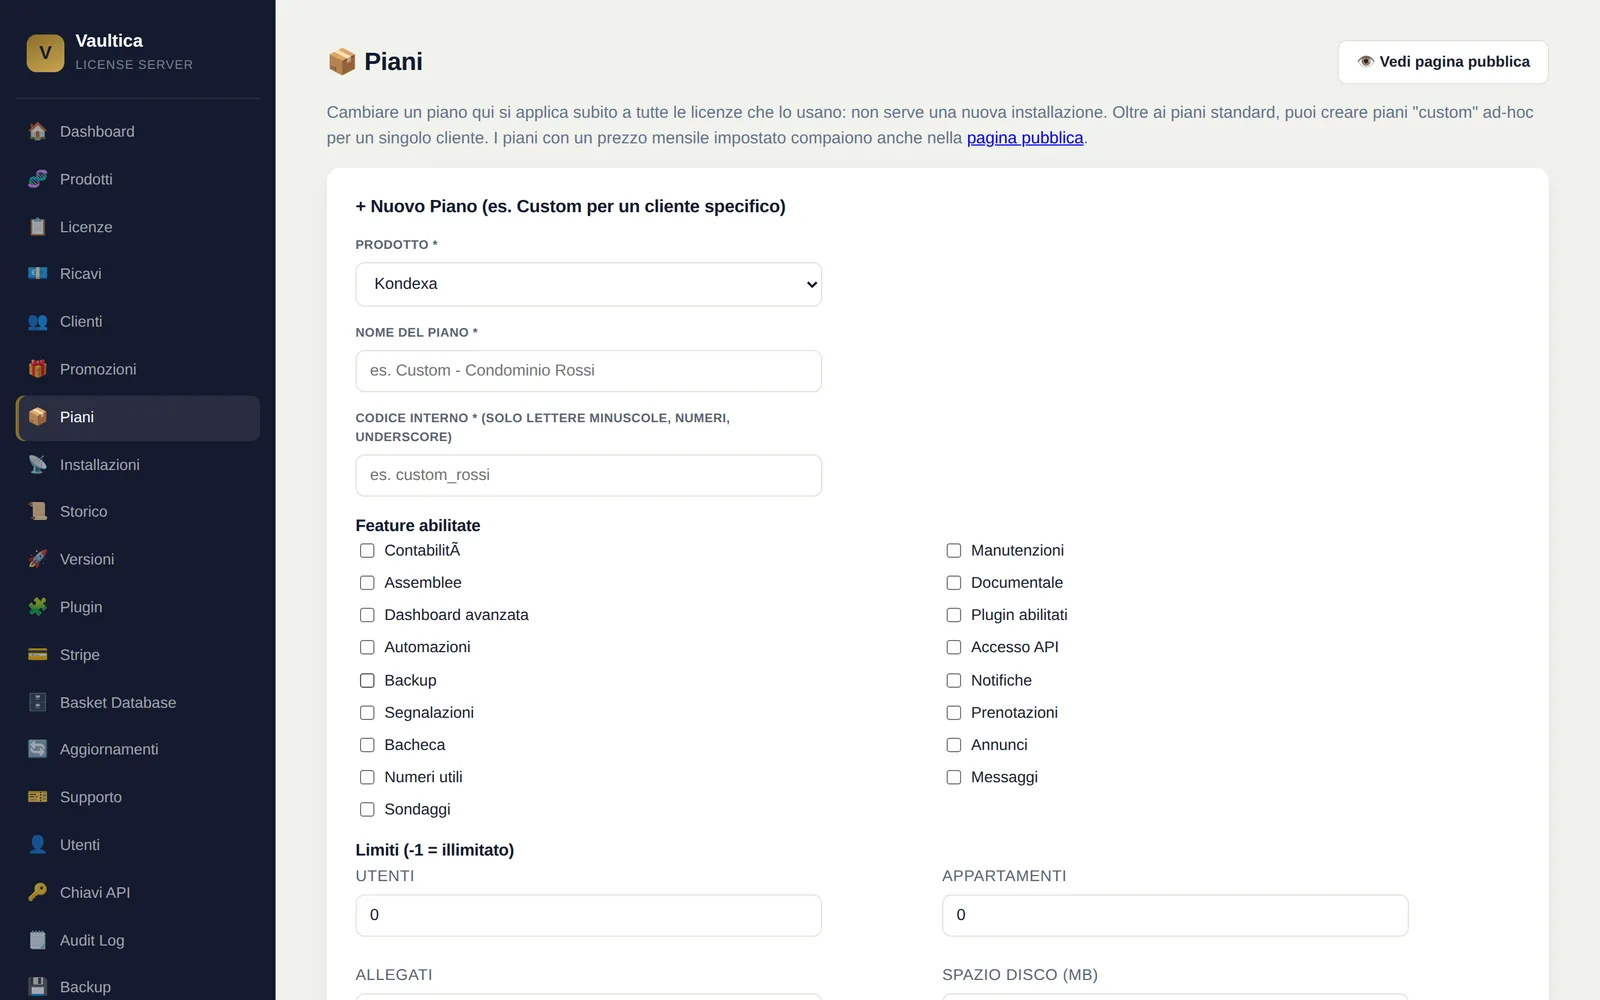
Plans, capacities and fields are defined per product: one server serves different applications without becoming four servers. The public plans page is built from the same data, so it cannot advertise a plan that does not exist.
- A plan per product, with its own capacities
- The public plans page comes from the same data
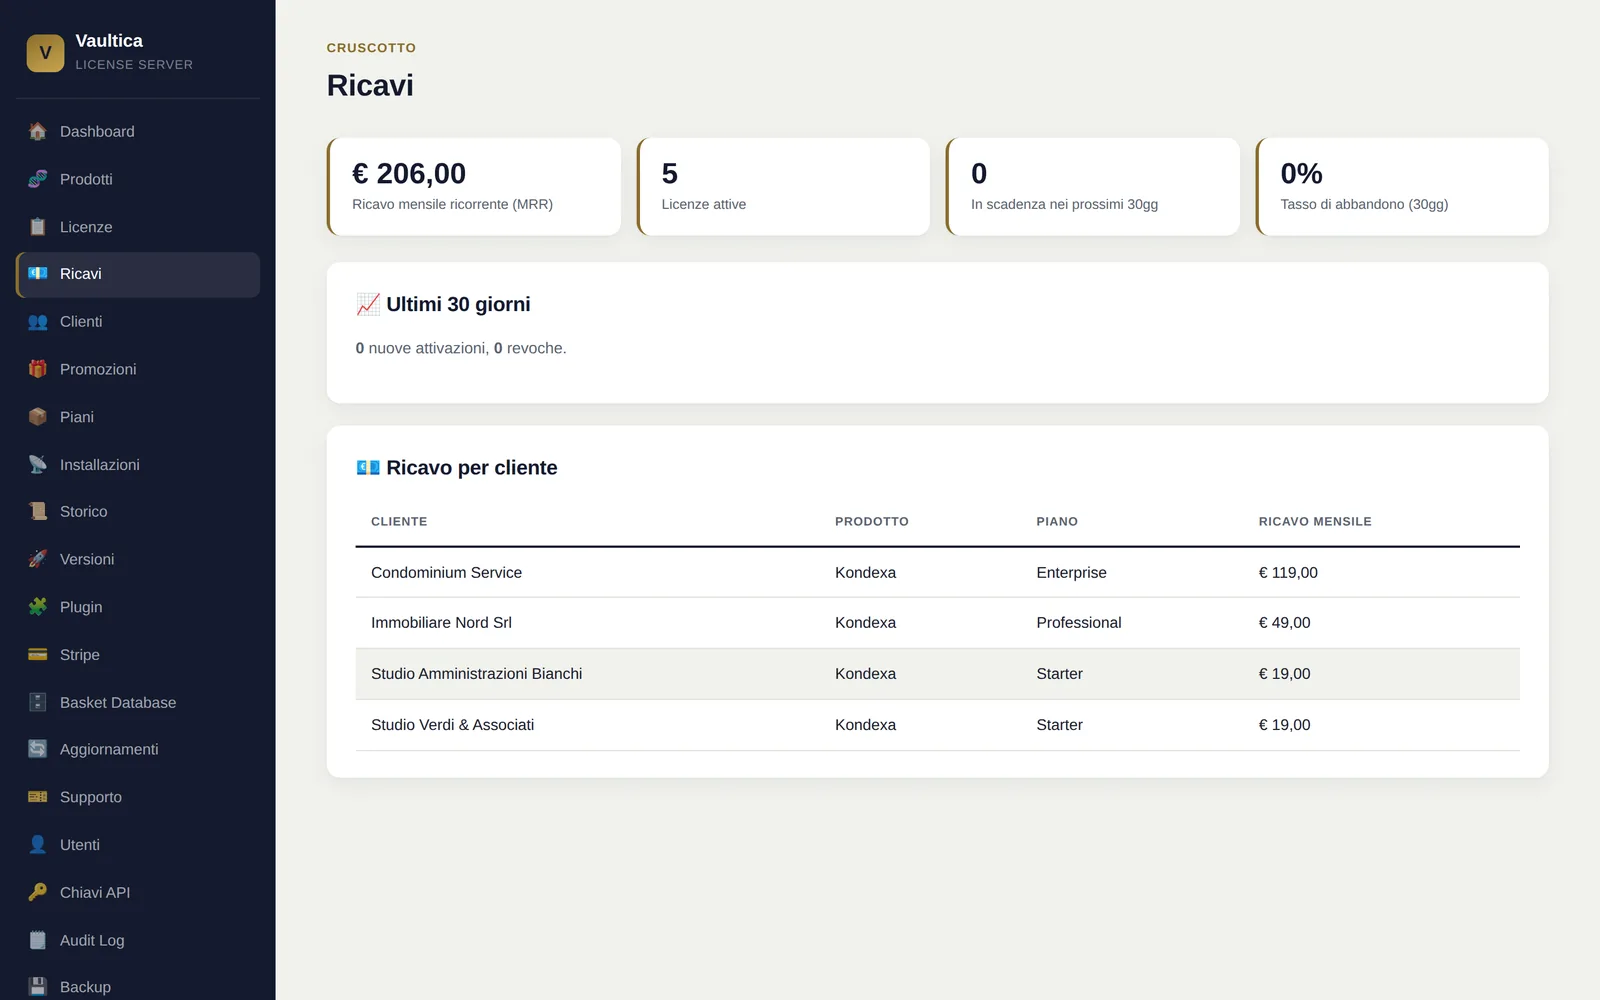
- Recurring revenue, by plan and by customer
Three areas
Whoever administers, buys or resells does not come in by the same door
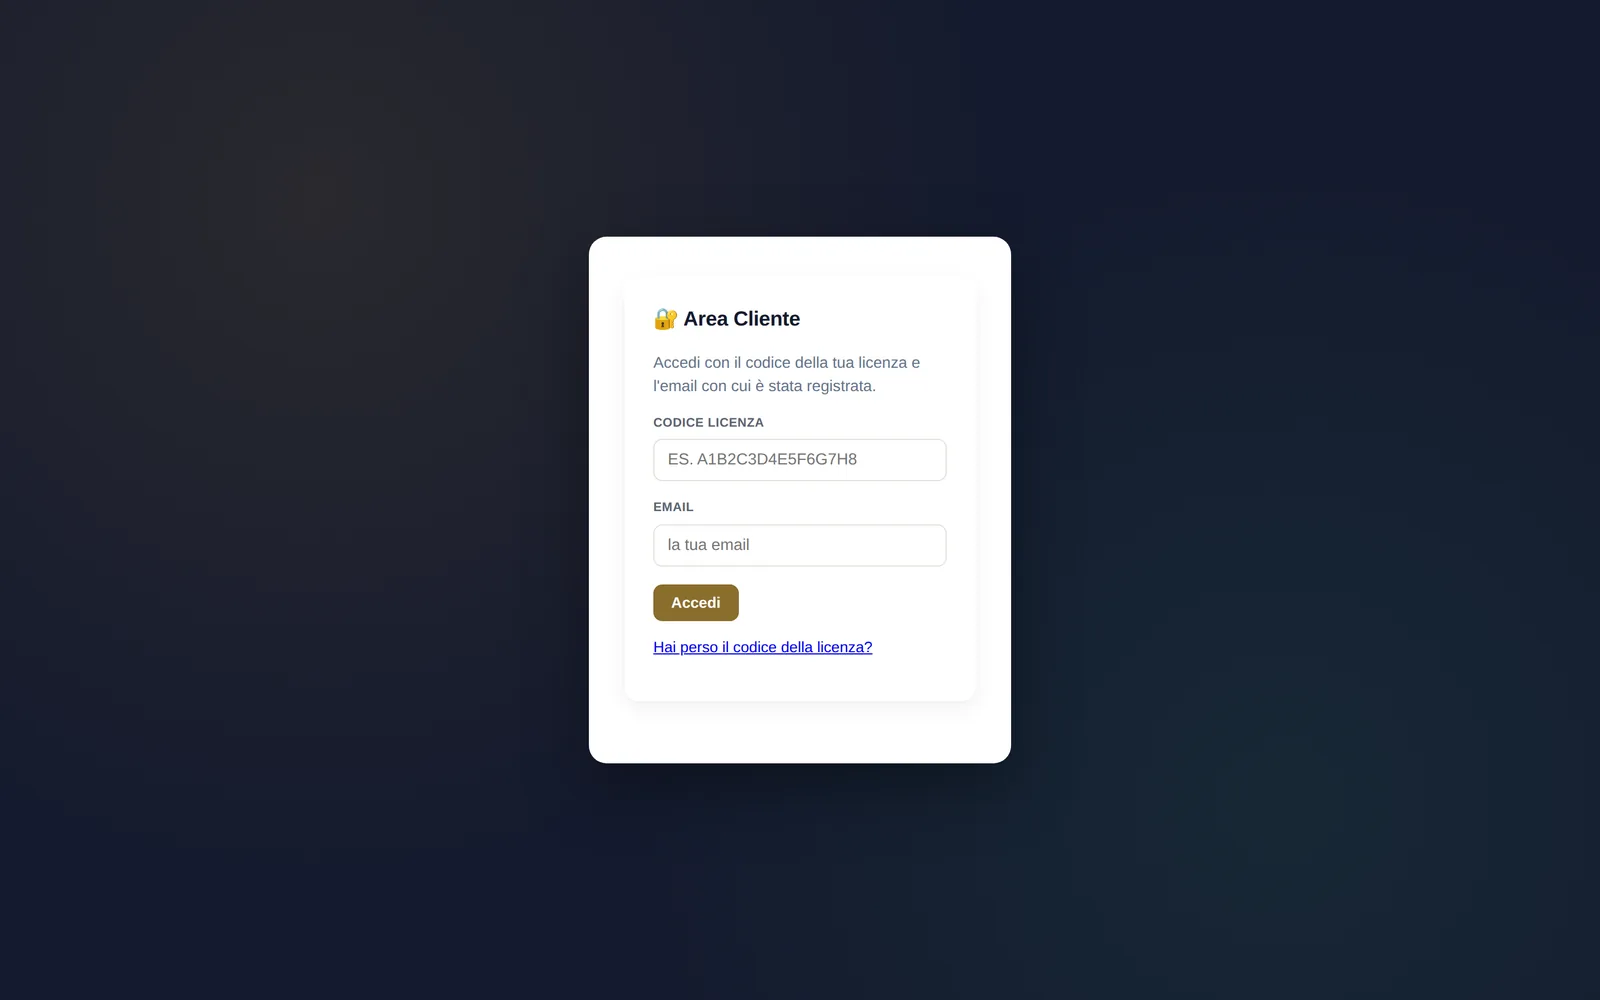
The administration panel, the customer portal and the reseller portal are three separate areas. A customer sees their own licences and their own installations, and nothing else.
- Customer portal: their licences and their installations
- Reseller portal, kept separate
- Administration panel for whoever issues
The signature is not a detail. It is the point.
A licence server that answers \u201cyes\u201d in the clear can be imitated by anyone in the middle. Here the response is signed with the private key, which never leaves the server, and the installed product is what verifies it.
Requirements
How it is put to work
PHP 8 and MySQL
PHP hosting with MySQL or MariaDB, like the products it serves.
One key pair
The server signs with the private key, the product verifies with the public one. The private key never leaves the server.
One server, several products
Plans, capacities and fields are defined per product: you do not need one Vaultica per application.
The other screens
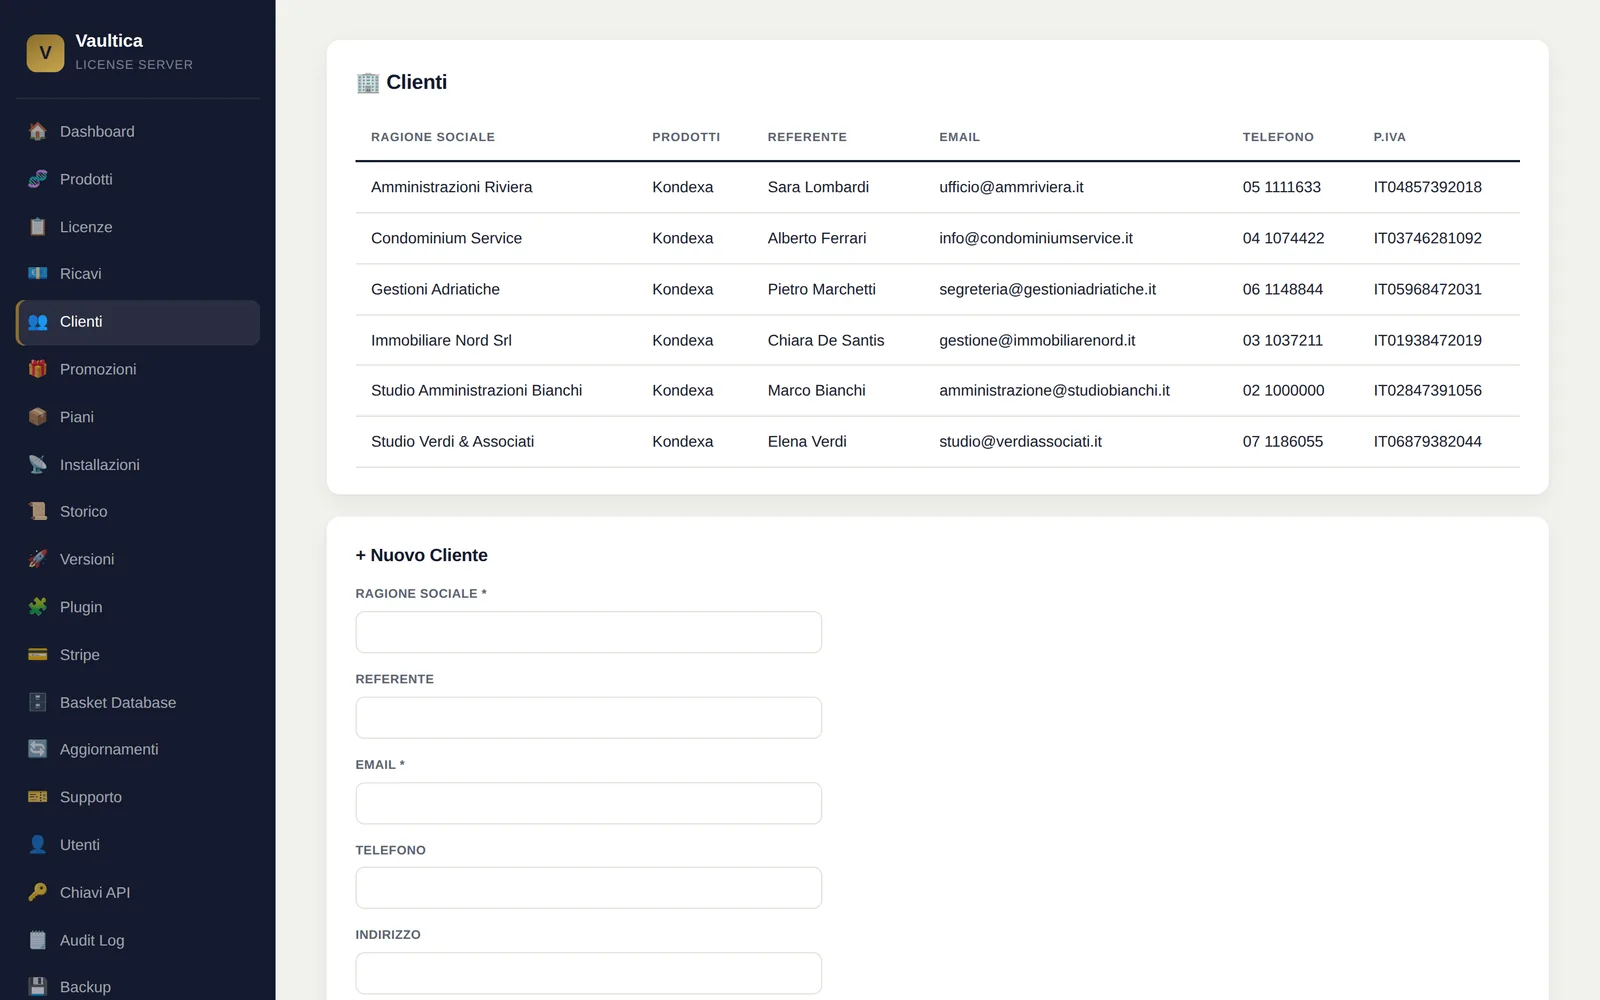
Images of the running application, with test data.
Frequently asked questions
How does the product know it can trust the response?
Because it checks. The server signs with the private key and the installed product verifies the signature with the public one: a response altered on the way does not pass.
Where is the private key?
On the server, and it never leaves it. Only the public key goes into the product, and that one verifies rather than signs.
Does every product need its own Vaultica?
No. Plans, capacities and fields are defined per product: one server serves several of them.
Can a customer see other customers' licences?
No. The customer portal, the reseller portal and the administration panel are three separate areas, and a customer sees their own licences and their own installations.
What hosting does it need?
PHP 8 with MySQL or MariaDB, like the products it serves. No build step and nothing to download.
Software gets sold. Then it has to be watched.
Who holds a licence, on which domain it runs, on what version and since when: without somewhere to look, you find out when something breaks.
Contact
Write to us
Tell us which product you are interested in and we will reply.